You signed in with another tab or window. Reload to refresh your session.You signed out in another tab or window. Reload to refresh your session.You switched accounts on another tab or window. Reload to refresh your session.Dismiss alert
{{ message }}
Repository navigation
fix(server): preserve Claude read-only MCP hints with native permission checks - #32230
An unrelated Claude MCP deny rule such as mcp__buildkite__create_build strips the read-only hint from Datadog graph helpers in Full Access threads. The card prompts repeatedly, and the adapter's conservative deny guard refuses the call. Fixes#32185.
Change
Use Claude's advertised mcp_call_check_permissions_v1 capability for read-only MCP App calls in Full Access when no possibly covering ask rule is present. Preserve their read-only hints and send check_permissions: true, so Claude evaluates the actual tool, hidden server aliases, and wildcards before execution.
Keep the conservative fallback for older CLIs, unreadable rules, ask rules, other permission modes, and tools without read-only annotations. Server-prefix overlap and normalized tool-name collision checks remain in place. No client, wire-schema, default, or model-facing instruction changes.
Scope and approval
This is a focused adapter fix for the reproducible cross-server downgrade in #32185. It qualifies for the small, obvious bug exception. It retains the hidden-alias protection deliberately added in #31131; it does not infer rule coverage from visible server names. The new path relies on Claude's native permission evaluator, observed against the actual installed runtime.
Verification
Windows, Node 26.12.1, pinned Claude Agent SDK 0.3.316, installed Claude CLI 2.1.319.
Test first, from apps/server: vp test run src/orchestration-v2/Adapters/ClaudeAdapterV2.test.ts -t "permission rules" --maxWorkers 1. Baseline: 22 passed and the new unrelated-deny case failed because readOnlyHint was absent. Fixed: 27 passed, including legacy alias handling, native-capability fallback, unreadable rules, ask rules, approval mode, and a tool without a read-only annotation.
Full selected tests, from apps/server: vp test run --passWithNoTests --maxWorkers 1 src/orchestration-v2/Adapters/ClaudeAdapterV2.test.ts src/provider/AgentContextBudget.test.ts: 348 passed, one existing Unix-only case skipped on Windows. Both files passed. All three selected package typechecks passed; the server recheck followed a test-only optional-property typing correction.
vp run check:changed origin/main --concurrency 1 hit the known Windows pnpm-junction input scan defect (perf(scripts): check:changed on Windows no longer spends minutes walking node_modules (2,500 s → 5.0 s) #32023) before stages, with repeated Filename too long errors. Ran every selected equivalent from scripts/check-changed.ts: changed-file format/lint, both unchanged Knip tasks, server generate --check, affected/dependent typechecks for t3, @t3tools/evals, and @t3tools/scripts, plus both selected test files. Checks ran serially with RAYON_NUM_THREADS=1; Knip used its supported KNIP_DISABLE_RAW_TRANSFER=1 transport with unchanged analysis. Tests used the owning server package to avoid the unrelated root browser-port issue (fix(web): browser tests no longer pick a port Windows has reserved #24007).
Integrated runtime verification used the production T3 CLI/server with isolated state, real project/thread commands, OAuth-authenticated WebSocket RPC, the production Claude adapter and actual SDK/CLI, and a native stdio MCP fixture. A loopback Anthropic HTTP/SSE fixture supplied synthetic model responses; Claude itself performed permission checks. No paid model turn or live userdata was used.
Separate no-model native CLI probes also confirmed that a matching ask invokes can_use_tool, while a checked matching deny refuses execution. The strict fallback remains necessary on runtimes without the capability. This verifies backend metadata and call enforcement; it does not claim a live Datadog account or macOS/browser visual pass.
Implemented with OpenAI GPT-6 via the Codex harness.
The reason will be displayed to describe this comment to others. Learn more.
Copilot was unable to review this pull request because the user who requested the review has insufficient remaining quota. Try requesting a review at a lower effort level.
Macroscope's review found this PR approvable — Read-only MCP card calls can retain their hints while using Claude's native permission checks. Capability, permission-mode, and rule gates limit the change, while unsupported paths retain existing conservative handling.
You can add or adjust custom eligibility rules. Learn more.
No actionable comments were generated in the recent review.
Walkthrough
The Claude adapter now evaluates when MCP app tools can use Claude-side permission checks. It conditionally exposes read-only hints and forwards permission-check requests for eligible calls. Tests cover capability, permission mode, rule, and tool-annotation conditions.
Changes: Claude MCP permission checks
Layer / File(s)
Summary
Permission-check eligibility and tool listings apps/server/src/orchestration-v2/Adapters/ClaudeAdapterV2.ts, apps/server/src/orchestration-v2/Adapters/ClaudeAdapterV2.test.ts
The adapter checks SDK capability, permission mode, and rules before exposing readOnlyHint. Tests cover unrelated deny rules, hidden aliases, unreadable rules, approval-required mode, and tools without read-only annotations.
Conditional permission checks on app calls apps/server/src/orchestration-v2/Adapters/ClaudeAdapterV2.ts, apps/server/src/orchestration-v2/Adapters/ClaudeAdapterV2.test.ts
The query-session call accepts optional checkPermissions. Eligible read-only tool calls set it, and the mcp_call control request includes check_permissions: true when requested. The local deny-rule guard remains for calls that do not use permission checks.
sequenceDiagram
  participant MCPApp
  participant ClaudeAdapterV2
  participant ClaudeAgentSdkQuerySession
  participant Claude
  MCPApp->>ClaudeAdapterV2: Request tool call
  ClaudeAdapterV2->>ClaudeAdapterV2: Check read-only annotation and permission eligibility
  ClaudeAdapterV2->>ClaudeAgentSdkQuerySession: Call tool with checkPermissions when eligible
  ClaudeAgentSdkQuerySession->>Claude: Send mcp_call with check_permissions when requested
Loading
Possibly related PRs
pingdotgg/t3code#24402: Changes how managed policy switches select bypassPermissions, a permission mode used by this PR’s eligibility checks.
Suggested labels:bugfix
Suggested reviewers:juliusmarminge
Merge Risk: Minimal · up to 5a749
No actionable issue remains from this review. The change is mergeable after normal checks.
Pre-merge checks: 4
Check name
Status
Explanation
Title check
The title clearly and concisely describes the main server change: preserving Claude read-only MCP hints through native permission checks.
Description check
The description includes all required sections and provides clear problem context, implementation details, scope justification, focused test results, runtime verification, and known limitations.
Linked Issues check
[#32185] The adapter enables Claude's mcp_call_check_permissions_v1 only for annotated read-only tools in Full Access, with readable rules and no possibly covering ask rule. It preserves `readOnly…
Out of Scope Changes check
The changes are limited to Claude MCP App permission evaluation, SDK request plumbing, and focused adapter tests. These changes directly support [#32185]. No unrelated client, wire-schema, default, or…
Full details: Linked Issues check
Explanation
[#32185] The adapter enables Claude's mcp_call_check_permissions_v1 only for annotated read-only tools in Full Access, with readable rules and no possibly covering ask rule. It preserves readOnlyHint and sends check_permissions: true for that path. Claude therefore evaluates unrelated, exact, and wildcard rules against the actual tool. The adapter retains the conservative deny guard for legacy, unreadable, approval-required, ask-rule, and non-read-only cases. Added tests cover the unrelated deny regression and these fallback cases.
Full details: Out of Scope Changes check
Explanation
The changes are limited to Claude MCP App permission evaluation, SDK request plumbing, and focused adapter tests. These changes directly support [#32185]. No unrelated client, wire-schema, default, or model-instruction changes are shown.
Finishing Touches
Generate unit tests (beta)
Create a new PR
Autofix · Keep fixing CodeRabbit findings and required CI, and resolving merge conflicts
Included review availability: This review used your included allowance. Your plan provides up to 10 included reviews per hour; 8 remain after this review.
Thanks for the scoped review. To clarify the existing runtime evidence: verification used an isolated production T3 CLI server, authenticated WebSocket mcpApps.toolInfo/callTool, the real Claude SDK and CLI 2.1.319, and a native stdio MCP fixture. A local Anthropic protocol fixture supplied the synthetic tool-use turn; it did not implement permission decisions. An unrelated deny allowed exactly one read-only MCP call, while exact and wildcard denies produced native Permission denied with zero MCP tool calls. A hidden-alias-shaped ask rule suppressed the read-only hint, and no app call was sent without approval.
This does not establish every hidden-alias deny spelling or a live Datadog/browser session. I am keeping that distinction explicit rather than treating the existing exact/wildcard cases as exhaustive hidden-alias qualification. The conservative alias/ask and legacy capability fallbacks remain in place; no broader runtime acceptance is claimed.
Evidence uses a synthetic local MCP graph fixture through the real Claude CLI and real T3 web app; Datadog itself was not available. Both sides used fresh isolated databases, Full Access, the same fixture, a 1280×800 viewport, and light theme.
Steps: configure an unrelated mcp__buildkite__create_build deny rule with no ask rules; request the native graph app; click Load / reload graph; confirm if prompted. Then deny mcp__graph__get_graph_data, start a new thread, and repeat.
AI-assisted; verified with the tests and tools listed above.
Not shown:
Datadog's actual MCP server and native graph were not exercised: no Datadog configuration or credentials were available. The observed before/after difference uses a clearly labeled synthetic MCP graph fixture.
Alias and wildcard deny matching were not exercised; the runtime denial check covered the actual helper's exact tool name.
This branch has not been deployed
No deployments
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
size:M30-99 changed lines (additions + deletions).vouch:unvouchedPR author is not yet trusted in the VOUCHED list.
4 participants
Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.


 github-actions
Bot
added
vouch:unvouched





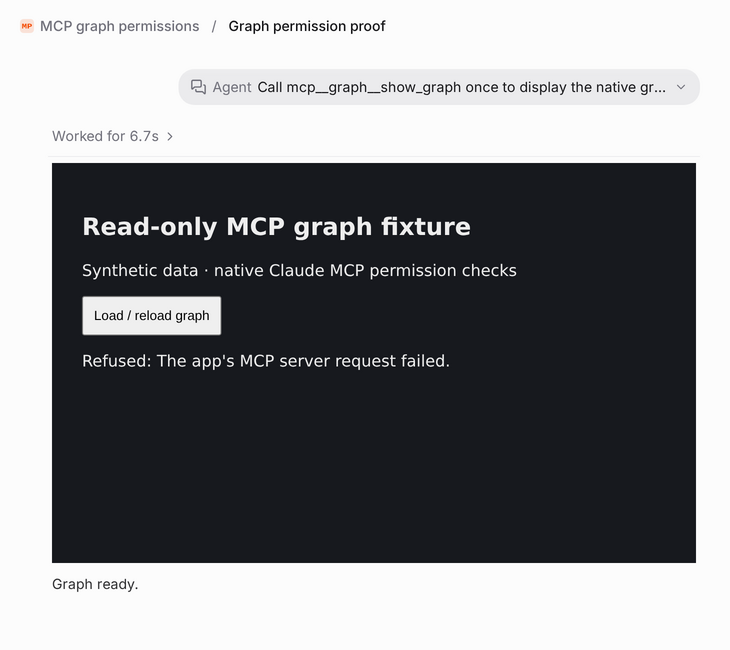
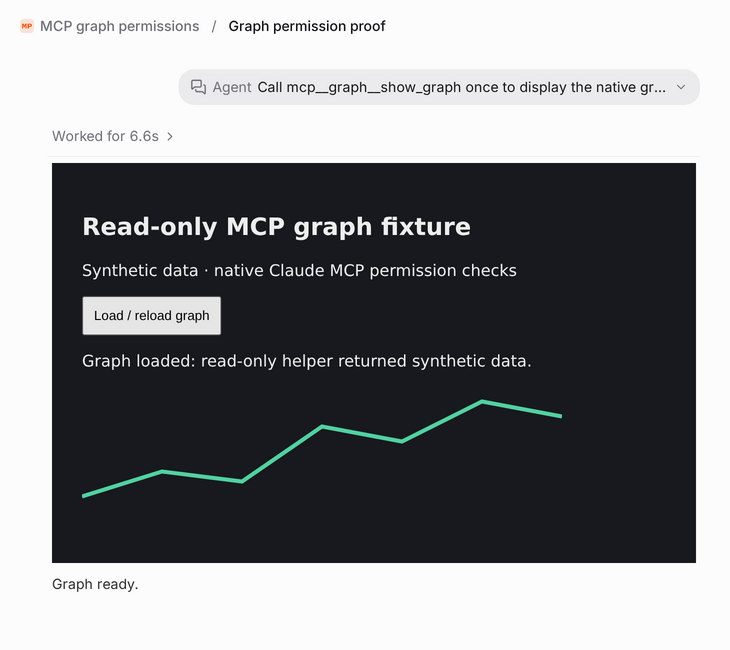
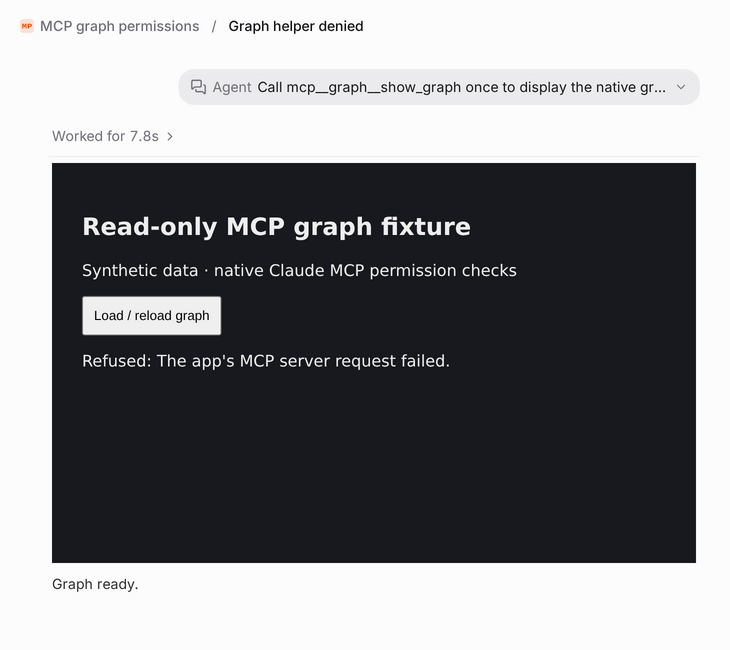
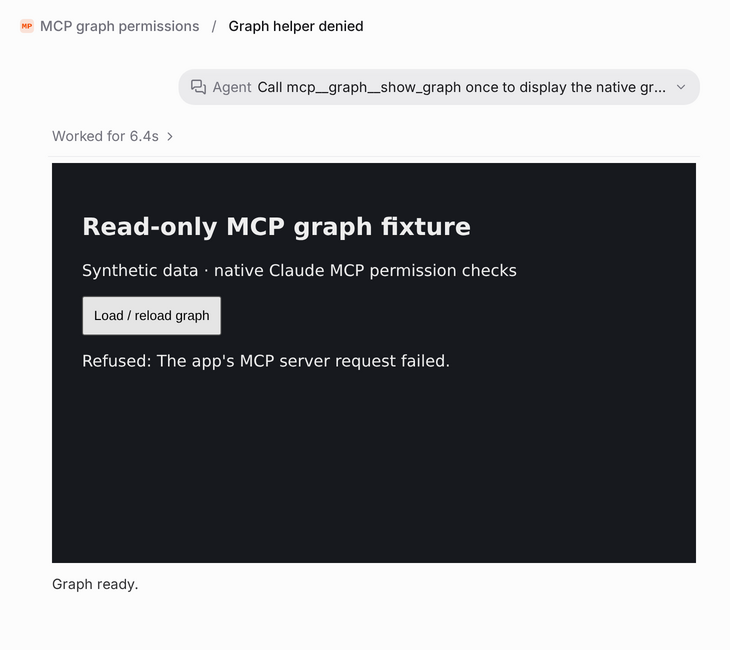


Problem
An unrelated Claude MCP deny rule such as
mcp__buildkite__create_buildstrips the read-only hint from Datadog graph helpers in Full Access threads. The card prompts repeatedly, and the adapter's conservative deny guard refuses the call. Fixes #32185.Change
Use Claude's advertised
mcp_call_check_permissions_v1capability for read-only MCP App calls in Full Access when no possibly covering ask rule is present. Preserve their read-only hints and sendcheck_permissions: true, so Claude evaluates the actual tool, hidden server aliases, and wildcards before execution.Keep the conservative fallback for older CLIs, unreadable rules, ask rules, other permission modes, and tools without read-only annotations. Server-prefix overlap and normalized tool-name collision checks remain in place. No client, wire-schema, default, or model-facing instruction changes.
Scope and approval
This is a focused adapter fix for the reproducible cross-server downgrade in #32185. It qualifies for the small, obvious bug exception. It retains the hidden-alias protection deliberately added in #31131; it does not infer rule coverage from visible server names. The new path relies on Claude's native permission evaluator, observed against the actual installed runtime.
Verification
Windows, Node 26.12.1, pinned Claude Agent SDK 0.3.316, installed Claude CLI 2.1.319.
apps/server:vp test run src/orchestration-v2/Adapters/ClaudeAdapterV2.test.ts -t "permission rules" --maxWorkers 1. Baseline: 22 passed and the new unrelated-deny case failed becausereadOnlyHintwas absent. Fixed: 27 passed, including legacy alias handling, native-capability fallback, unreadable rules, ask rules, approval mode, and a tool without a read-only annotation.apps/server:vp test run --passWithNoTests --maxWorkers 1 src/orchestration-v2/Adapters/ClaudeAdapterV2.test.ts src/provider/AgentContextBudget.test.ts: 348 passed, one existing Unix-only case skipped on Windows. Both files passed. All three selected package typechecks passed; the server recheck followed a test-only optional-property typing correction.vp run check:changed origin/main --concurrency 1hit the known Windows pnpm-junction input scan defect (perf(scripts): check:changed on Windows no longer spends minutes walking node_modules (2,500 s → 5.0 s) #32023) before stages, with repeatedFilename too longerrors. Ran every selected equivalent fromscripts/check-changed.ts: changed-file format/lint, both unchanged Knip tasks, servergenerate --check, affected/dependent typechecks fort3,@t3tools/evals, and@t3tools/scripts, plus both selected test files. Checks ran serially withRAYON_NUM_THREADS=1; Knip used its supportedKNIP_DISABLE_RAW_TRANSFER=1transport with unchanged analysis. Tests used the owning server package to avoid the unrelated root browser-port issue (fix(web): browser tests no longer pick a port Windows has reserved #24007).Integrated runtime verification used the production T3 CLI/server with isolated state, real project/thread commands, OAuth-authenticated WebSocket RPC, the production Claude adapter and actual SDK/CLI, and a native stdio MCP fixture. A loopback Anthropic HTTP/SSE fixture supplied synthetic model responses; Claude itself performed permission checks. No paid model turn or live userdata was used.
Separate no-model native CLI probes also confirmed that a matching ask invokes
can_use_tool, while a checked matching deny refuses execution. The strict fallback remains necessary on runtimes without the capability. This verifies backend metadata and call enforcement; it does not claim a live Datadog account or macOS/browser visual pass.Implemented with OpenAI GPT-6 via the Codex harness.